
Under AIGP BoK v2.1, the 85 scored questions fall roughly as follows: Domain I (Foundations) 16–20, Domain II (Laws, standards and frameworks) 19–23, Domain III (Governing AI development) 21–25 and Domain IV (Governing AI deployment and use) 21–25. Domains III and IV together are about half the exam. Give them about half your practice time, even if Domain II feels like the hardest reading.
The AIGP blueprint tells you exactly how IAPP spreads questions across the exam. Most candidates still study by instinct, so lawyers spend weeks on the EU AI Act and engineers spend weeks on model types. Allocating time by weight, then adjusting for your own gaps, is the simplest way to raise your score.
AIGP domain weights at a glance
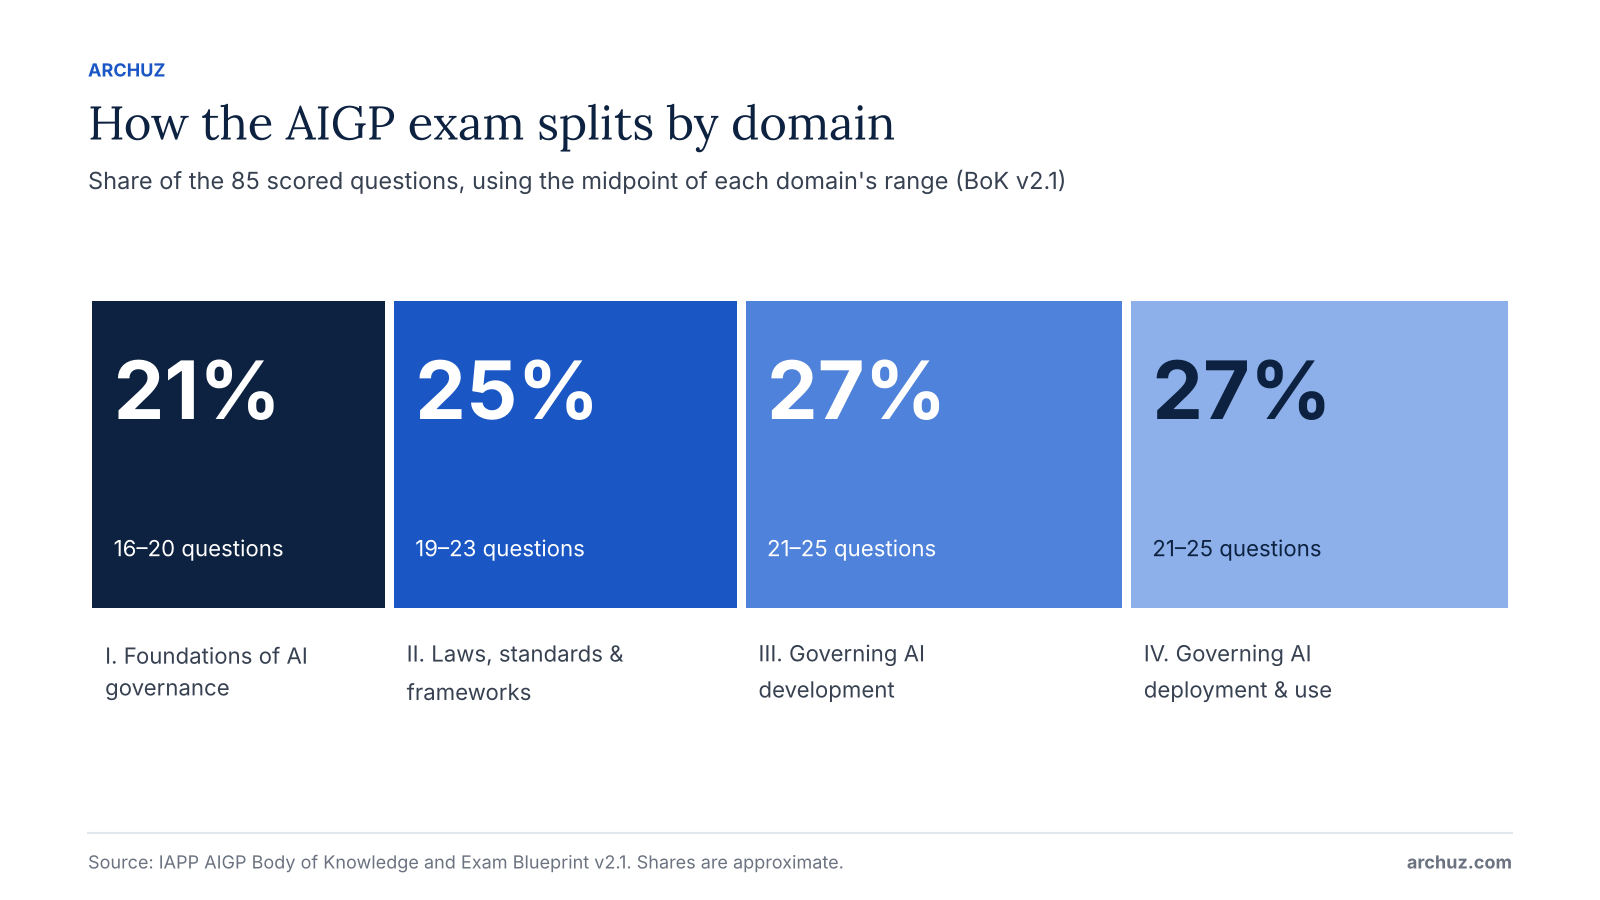
| Domain | Scored questions (approx.) | Share of scored exam |
|---|---|---|
| I. Understanding the Foundations of AI Governance | 16–20 | ~19–24% |
| II. Understanding How Laws, Standards and Frameworks Apply to AI | 19–23 | ~22–27% |
| III. Understanding How to Govern AI Development | 21–25 | ~25–29% |
| IV. Understanding How to Govern AI Deployment and Use | 21–25 | ~25–29% |
Ranges come from the BoK v2.1 blueprint as reported by IAPP training partners. Confirm them against the current BoK PDF from IAPP. The ranges overlap, so your exact form will vary.
What each domain covers
Domain I – Foundations of AI governance
- What AI and machine learning are; types of models; generative and general-purpose AI.
- AI risks and harms to individuals, groups, organisations and society.
- Responsible AI principles; governance structures, roles and policies.
- The AI lifecycle and where governance fits in.
Domain II – Laws, standards and frameworks
- How existing law applies to AI: privacy and data protection, anti-discrimination, consumer protection, product liability, intellectual property.
- AI-specific laws (II.C, about 6–8 questions): the EU AI Act plus, under v2.1, other AI laws such as South Korea's AI Basic Act and US laws.
- Standards and tools (II.D, about 3–5 questions): ISO/IEC 42001, ISO/IEC 42005, the NIST AI RMF and other frameworks.
Domain III – Governing AI development
- Defining the business case, intended use and risk classification.
- Data governance: sourcing, quality, lawful use, bias, documentation.
- Training, testing, validation, red teaming and release decisions.
- Documentation such as model cards, technical files and impact assessments.
Domain IV – Governing AI deployment and use
- Procurement and third-party risk; contracts.
- Deployment readiness, human oversight, user transparency.
- Monitoring, incident management, change management and decommissioning.
- Agentic architectures (new indicator IV.A.3 in v2.1).
How to allocate your study hours
Start with the blueprint weights, then shift time towards your gaps:
| Background | Domain I | Domain II | Domain III | Domain IV |
|---|---|---|---|---|
| Baseline (by weight) | 20% | 25% | 27% | 28% |
| Privacy / legal professional | 25% | 15% | 30% | 30% |
| Data scientist / engineer | 10% | 40% | 22% | 28% |
| Risk / audit / GRC | 25% | 30% | 22% | 23% |
| New to both | 25% | 25% | 25% | 25% |
These are Archuz recommendations. Use your diagnostic results to adjust them.
The topics inside each domain
Domain I: Foundations of AI governance (16–20 questions)
- What AI is: machine learning, deep learning, generative AI, agentic AI; training, inference and the AI lifecycle
- AI harms to individuals, groups, organisations and society
- Responsible AI principles (OECD, UNESCO and similar)
- Governance roles, accountability, policies and culture
- AI literacy and training
Domain II: Laws, standards and frameworks (19–23 questions)
- How existing laws apply to AI: privacy and data protection, anti-discrimination, consumer protection, product liability, intellectual property
- AI-specific laws: the EU AI Act in depth, plus other AI laws such as South Korea's AI Basic Act and US federal and state approaches (broadened in v2.1)
- Standards and frameworks: the NIST AI RMF, ISO/IEC 42001, ISO/IEC 42005 (added in v2.1) and others
Domain III: Governing AI development (21–25 questions)
- Defining the use case, business case and risk appetite
- Data governance: provenance, quality, representativeness, consent and licensing
- Impact and risk assessments during design
- Testing and validation: performance, fairness, robustness, red teaming
- Documentation, release readiness and sign-off
Domain IV: Governing AI deployment and use (21–25 questions)
- Deciding whether to buy or build; vendor due diligence and contracts
- Deployer responsibilities, human oversight and transparency to users
- Monitoring for drift, incidents and misuse
- Agentic architectures and their controls (added in v2.1)
- Updating, retraining and decommissioning systems
NIST AI RMF: the detail the exam expects
| Function | Purpose | Examples of activities |
|---|---|---|
| Govern | Cross-cutting culture, policies and accountability | Policies, roles, risk tolerance, workforce diversity, third-party risk policies |
| Map | Understand context and identify risks | Intended use, stakeholders, categorising the system, mapping impacts |
| Measure | Analyse and track risks | Metrics, testing, evaluating trustworthiness characteristics |
| Manage | Prioritise and act on risks | Treatment decisions, response and recovery, monitoring third-party risks |
Also know the seven trustworthiness characteristics: valid and reliable; safe; secure and resilient; accountable and transparent; explainable and interpretable; privacy-enhanced; and fair with harmful bias managed. The Generative AI Profile (NIST AI 600-1, July 2024) applies the framework to generative AI risks. See the NIST AI RMF explained.
Four domain-weight practice questions
Original Archuz questions, not real exam items.
Before training a model on customer support transcripts, what should governance confirm first?
- AIts lawful basis and rights to use the data for training, and whether the data is fit for purpose
- BThat the transcripts are encrypted while stored for training
- CThat the vendor's model card describes its own training data
- DThat customers will be told about the new AI feature at launch
Show answer
Correct: A — Its lawful basis and rights to use the data for training, and whether the data is fit for purpose
Before training, governance confirms the data may be used for this purpose and is suitable (A). Encryption (B) protects the data but doesn't make the use lawful. The vendor's model card (C) is about the base model, not your transcripts, and telling customers at launch (D) comes too late to decide whether training was permitted.
A vendor updates the model behind a tool you deploy. What should your governance process require?
- ANo action, because the vendor is responsible for its own model
- BChange notification and a proportionate re-assessment before relying on the new version
- CTerminate the contract and run a new procurement
- DMonitor user complaints and act if they increase
Show answer
Correct: B — Change notification and a proportionate re-assessment before relying on the new version
A deployer stays responsible for its use of the tool, so a model change triggers proportionate re-assessment (B). Leaving it to the vendor (A) ignores the deployer's own duties, termination (C) is disproportionate as a default, and waiting for complaints (D) finds problems only after harm.
Which document is a voluntary framework rather than a law?
- AThe EU AI Act
- BColorado's AI Act
- CThe NIST AI RMF
- DSouth Korea's AI Basic Act
Show answer
Correct: C — The NIST AI RMF
The NIST AI Risk Management Framework is a voluntary framework (C). The EU AI Act (A), Colorado's AI Act (B) and South Korea's AI Basic Act (D) are all legislation, even where their application dates have been phased or delayed.
Which is an example of a societal AI harm?
- AA chatbot giving one customer an incorrect answer
- BA model leaking one employee's personal data
- CLarge-scale misinformation undermining trust in elections
- DA company losing revenue after a faulty AI rollout
Show answer
Correct: C — Large-scale misinformation undermining trust in elections
Harms are often grouped as individual, group, organisational and societal. Election misinformation damages democratic institutions and public trust: a societal harm (C). A wrong answer (A) and a data leak (B) harm individuals, and lost revenue (D) is an organisational harm.
Using your score report to re-weight
After a practice mock, or a failed attempt, look at your results by domain:
- Find the domain where you're furthest below 75%.
- Multiply that gap by the domain's weight. A 15-point gap in Domain IV costs more than a 15-point gap in Domain I.
- Give the next week's hours to the domain with the largest weighted gap.
Common allocation mistakes
- Treating Domain II as the EU AI Act chapter. Under v2.1, AI-specific law is only 6–8 questions and includes non-EU laws. See how much of the AIGP is the EU AI Act.
- Skipping Domain I because it seems basic. Foundation questions on risk types, roles and terminology can be subtle.
- Ignoring the new v2.1 indicators. Agentic AI and ISO/IEC 42005 are low-volume but easy points if you've prepared. See BoK v2.1 changes.
For Domain II in depth, see the AIGP Domain II deep dive.
See your score by domain before the real exam
The AIGP Complete Pack's 300 questions are tagged by BoK v2.1 domain, so your practice results show exactly where to spend your remaining hours.
Get the Complete PackFrequently asked questions
What are the AIGP domain weights?
Under BoK v2.1 there are about 16–20 scored questions for Domain I, 19–23 for Domain II, 21–25 for Domain III and 21–25 for Domain IV.
Which AIGP domain is the largest?
Domains III (governing development) and IV (governing deployment and use) are the largest, at about 21–25 scored questions each.
Did the domain weights change in v2.1?
The four domains stayed the same. Within Domain II, AI-specific laws rose from 5–7 to 6–8 questions, and standards and tools fell from 4–6 to 3–5.
Does every domain need a passing score?
No. You need an overall scaled score of 300. Domain results are diagnostic, but a very weak high-weight domain makes passing much harder.
What are the NIST AI RMF functions on the AIGP?
Govern, Map, Measure and Manage. Govern is cross-cutting and supports the other three. The exam often asks which function a given activity belongs to.
What was added to the AIGP domains in v2.1?
BoK v2.1 broadened legal coverage from the EU AI Act to AI-specific laws generally, added ISO/IEC 42005 on impact assessment, and added agentic AI architectures to Domain IV.
Sources
- IAPP: AIGP Body of Knowledge
- Training Camp: AIGP learning path around BoK v2.1 (domain question ranges)
- Privacy Bootcamp: AIGP Body of Knowledge 2026 (competency changes)
Last reviewed: October 2026.