CIPP/E COMPLETE PACK · TITLE 02
The CIPP/E rewards precise law applied to precise facts. This pack trains that precision, then shows you how to turn the credential into an appointment, a title and a band.
Why good candidates fail it
Most wrong options on the CIPP/E aren't nonsense. They state a real rule of the GDPR, the ePrivacy Directive or the case law, but one whose trigger isn't met, which belongs to a different instrument, or which doesn't answer the question asked. Candidates who half-know the material pick them. The fix is to know the distinctions cold and to read every scenario for the fact that decides it.
The exam at a glance
| Questions | 90 |
| Time | 2½ hours, closed book |
| Scoring | Scaled 100–500; 300 to pass |
| Domains | Five, with Domain II alone carrying up to 28 questions |
| Fee | $550 first IAPP exam; $375 if you already hold an IAPP credential |
What's inside
The most comprehensive guide in the series. All five domains run in blueprint order, with framework tables that settle the distinctions the exam exploits. Exam Trap, Definition and Currency callouts flag the points older material now gets wrong.
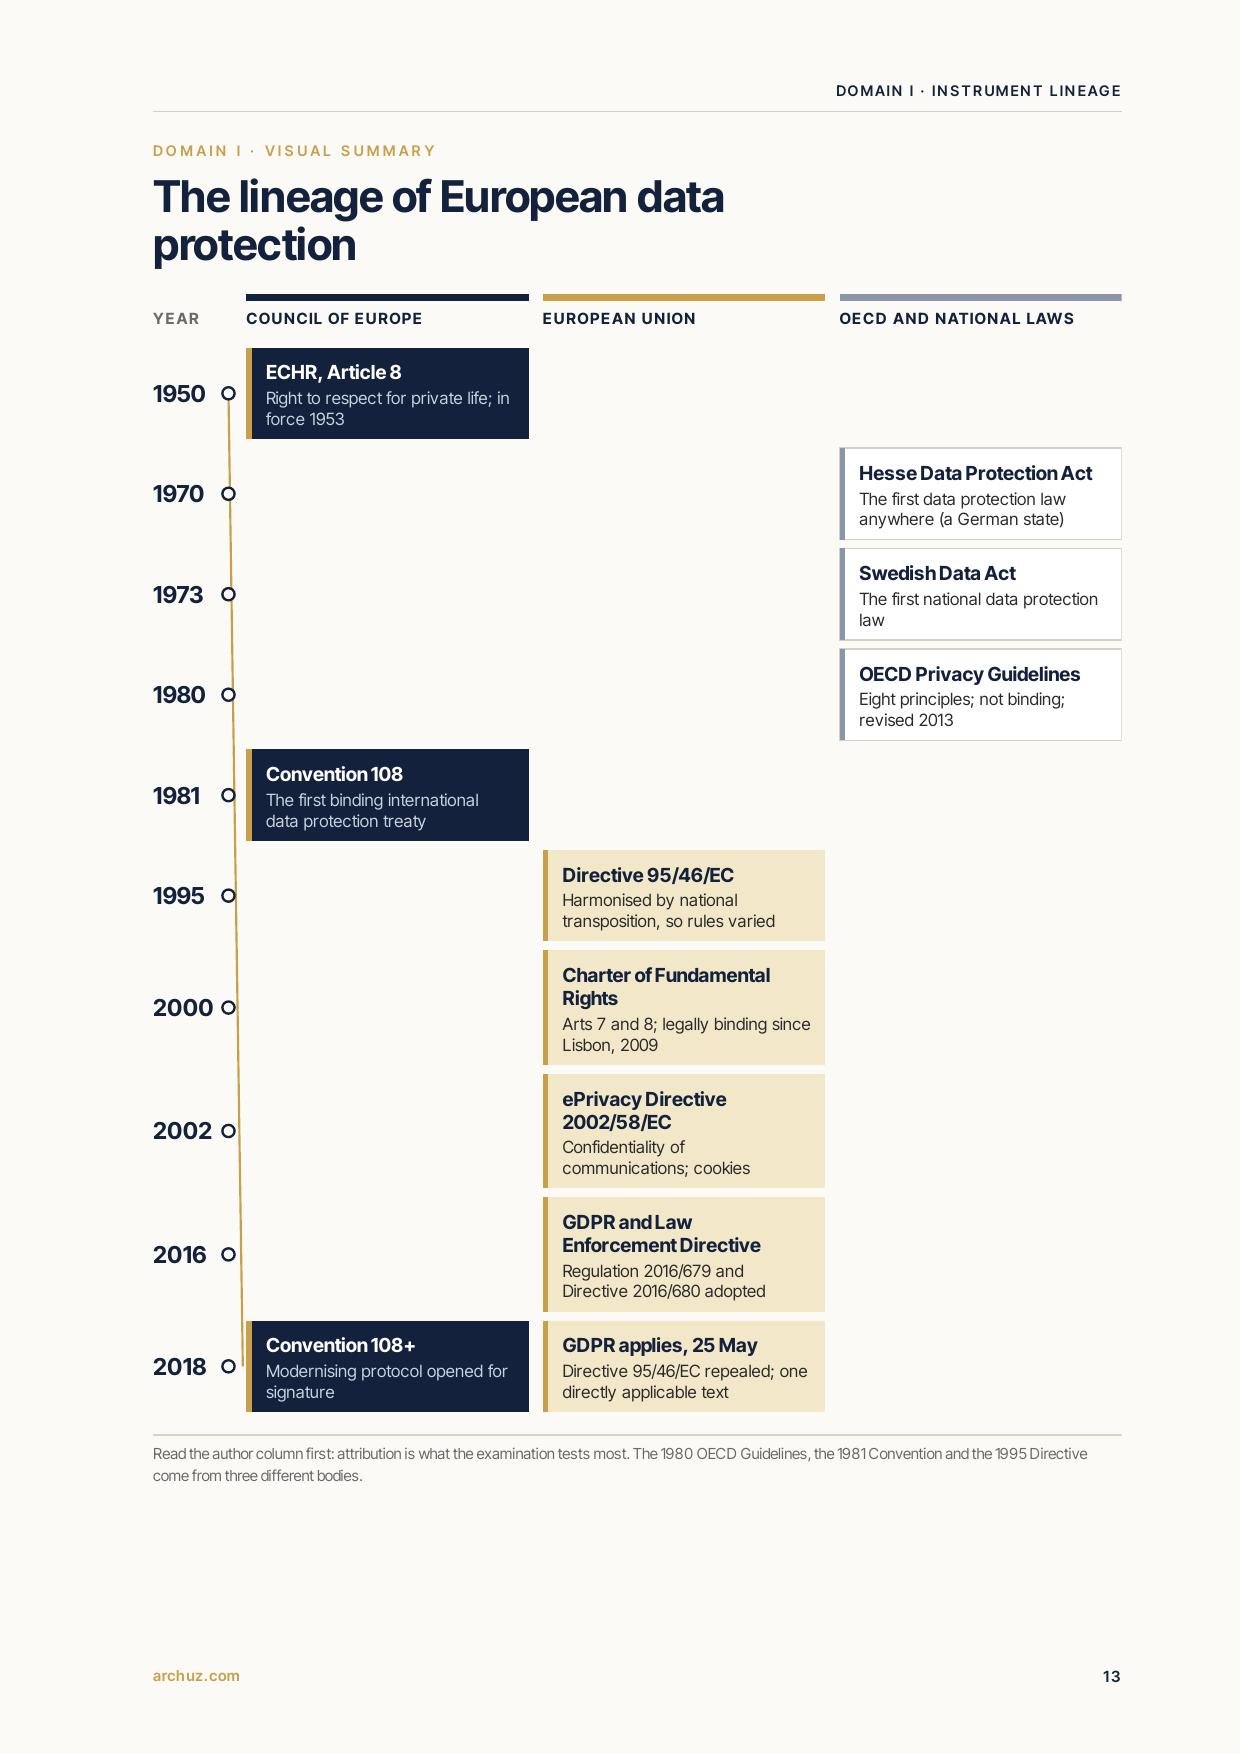
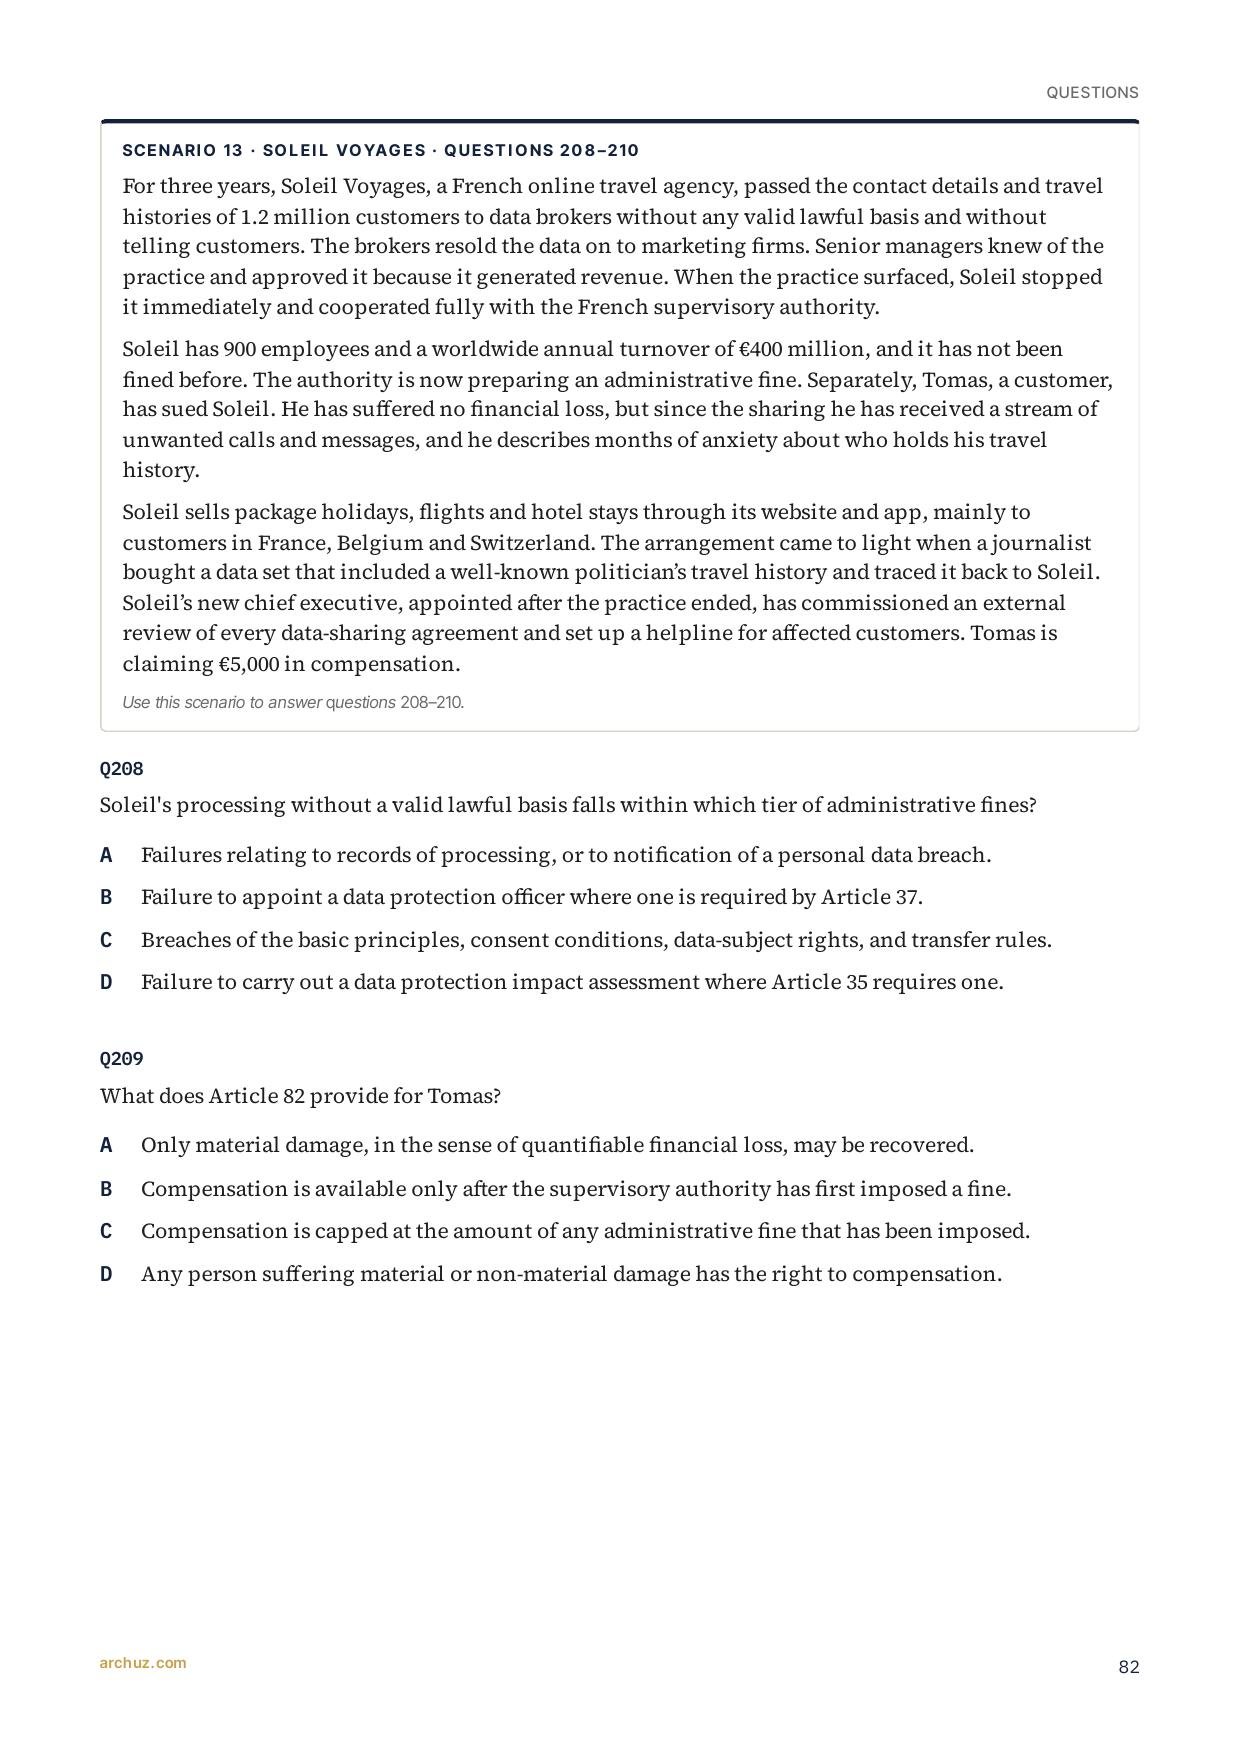
The six question types the CIPP/E uses, in roughly exam proportions. 220 of the 300 are scenario, scenario-block and best-option questions; 18 scenario blocks test one set of facts from several legal angles.
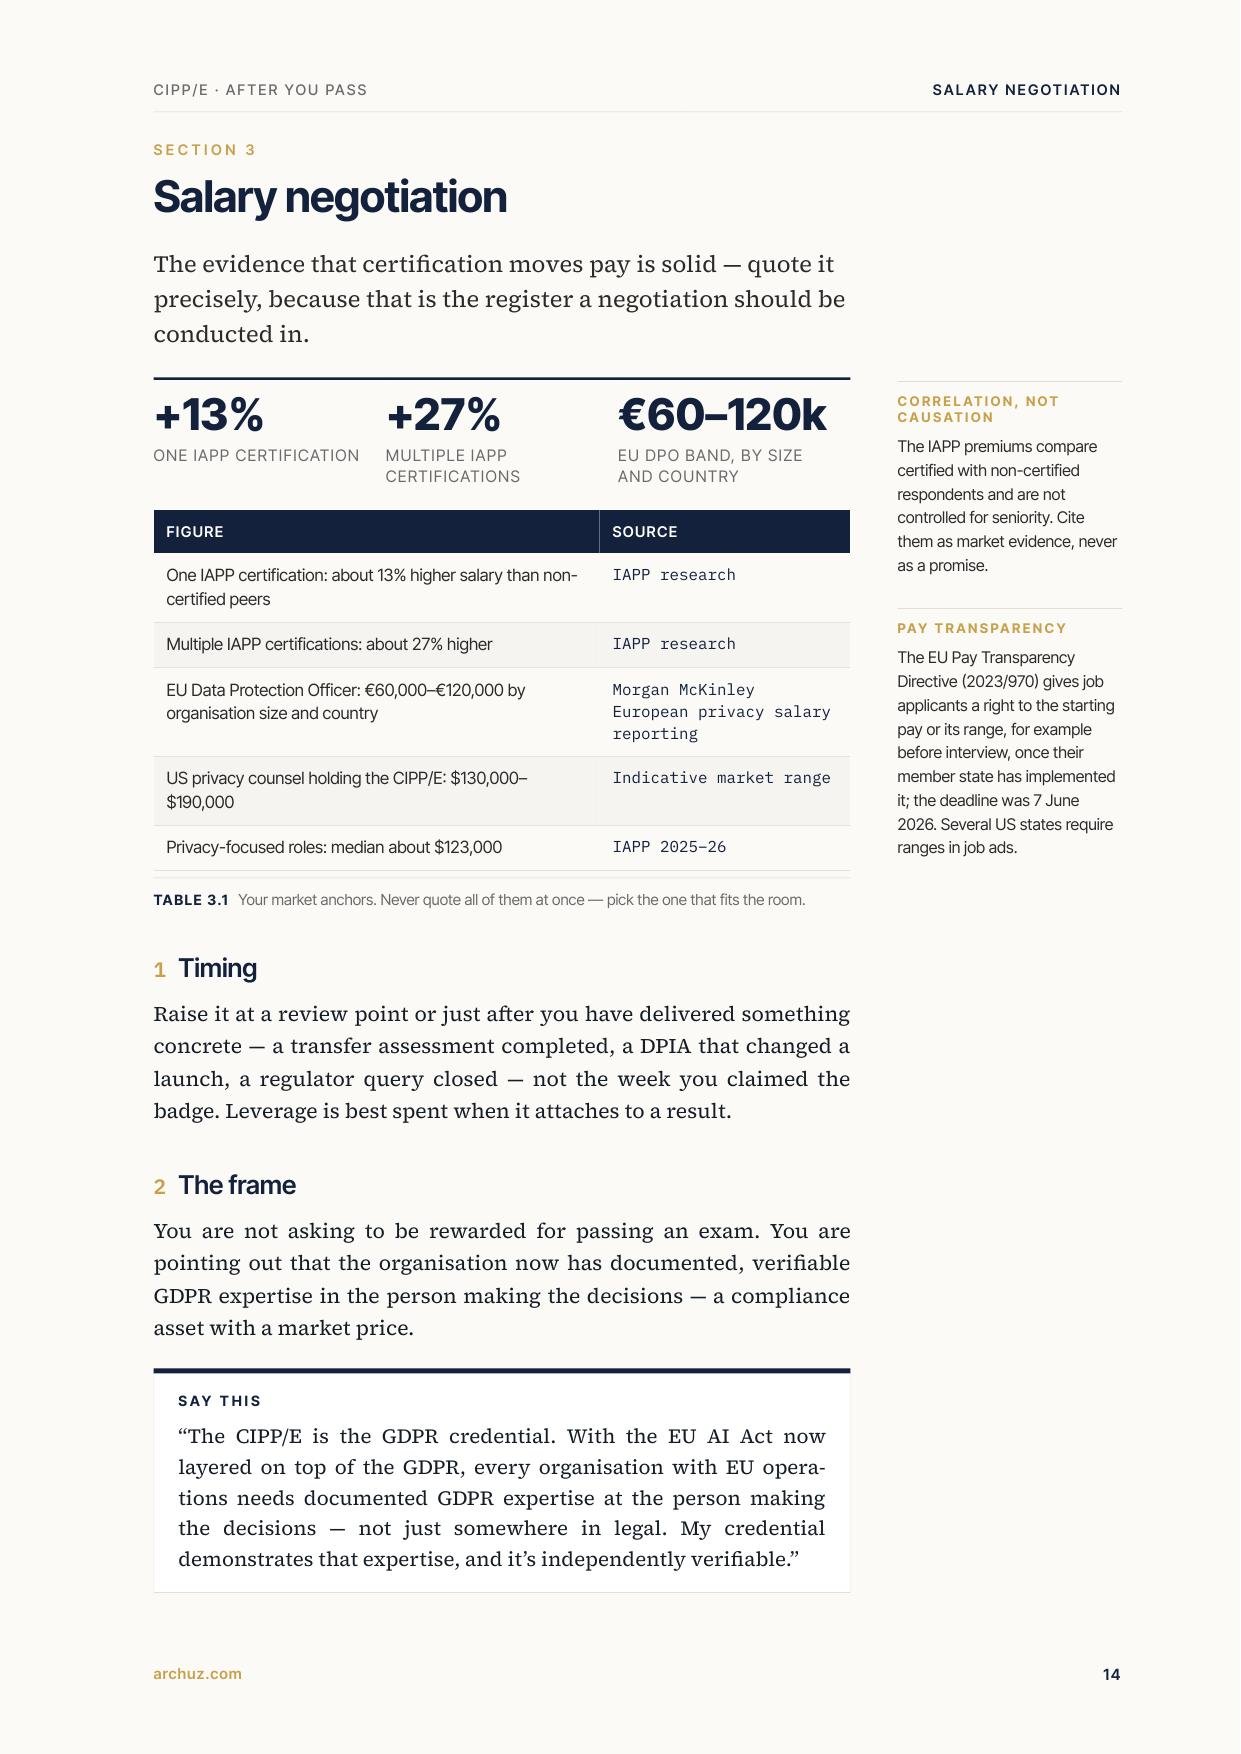
The first 24 hours, including putting the certificate on the DPO file under Art. 37(5). LinkedIn and CV rewrites for the DPO, counsel, compliance and analyst tracks, and salary evidence for EU and US markets.
Inside the pack
How to use it
Pick your reading path. Four weeks out, read straight through. One week out, read only the tables, traps and rapid-recall pages.
Drill the bank by domain, untimed, and study every explanation.
Work timed blocks of ninety at 100 seconds a question. A score of 80% or better on a timed block, with the explanations understood, is a reasonable signal to book.
Who it's for
It's for DPOs and people who want the appointment, privacy counsel and lawyers moving into data protection, and compliance, audit and risk people who need the credential a job title alone can't prove.
It isn't a video course or a live class. It's a reading-and-practice method for people who study on their own.
Common questions
What people say
Other materials write "see GDPR Chapter III." This guide opens every explanation with the exact article — Article 6(1)(b), Article 35(1), Article 46(2)(c). When the wrong options are also real GDPR rules, that precision matters. The question bank was the strongest I tried for the CIPP/E.
I failed the CIPP/E first time because I treated the GDPR as the complete picture. The ePrivacy Directive overrides the GDPR on several things — electronic communications, cookie consent, marketing — and the exam tests the boundary precisely. The cram guide covers ePrivacy with the same depth as the GDPR, including where it overrides and where it defers. Passed the retake clearly.
The guide has a section on command words — the verbs the CIPP/E uses in question stems and what type of answer each signals. Assess means identify the applicable rule and its threshold. Advise means give a specific, actionable recommendation. Determine means reach a conclusion from the facts, not from general knowledge. Reading those distinctions changed how I approached every stem. Passed comfortably.
The guide covers the Data Privacy Framework and the Latombe judgment in September 2025 upholding the adequacy decision. Most materials were still hedging on this. The cram guide stated the current position clearly and explained what to promote for if there is an appeal. I had two questions on the adequacy landscape in the real exam and knew both answers because of this coverage.
I used it for exam prep and still use it in client meetings when I need to cite something quickly. There are some formatting inconsistencies in the PDF on my reader.
International transfers is one of the most tested areas on the CIPP/E and one of the most confusing because the logic branches — adequacy, SCCs with TIA, derogations. The transfer decision table in the guide walks through the five steps in order. I had four transfer questions in the real exam and worked through the table for each one.
The CIPP/E After You Pass guide has a full lawful basis register template — field by field, with examples and a note on what the IAPP calls the practical tip for each field. I built a version of it for my organisation two weeks after passing and brought it to my first post-exam review meeting. The toolkit section turns the exam content into working documents rather than just knowledge.
The toolkit has the full Article 28(3) checklist — every term the contract must include, with a practical note on what to look for. I had memorised it and had a question in the exam testing which term was missing from a described processor contract. Got it right immediately.
The gold Exam Trap boxes throughout the cram guide mark the exact places where outdated or incomplete knowledge costs marks — a changed threshold, a distinction the GDPR makes that the exam exploits, a rule that only applies in a specific context. I had around 8 questions in the real paper where I recognised the trap as I was reading the stem. The guide had flagged each of them explicitly.
I used the Archuz CIPM guide six months earlier. Same reading method structure, completely different content. The domain PI maps, the Exam Trap callouts, the distractor teardowns all worked the same way. By week two on the CIPP/E I was already scoring higher than I had by week four on the CIPM. Method transfer is real and it speeds everything up.
The five examination scenarios at the end of the cram guide each have every wrong option pulled apart and explained. I worked through all five before opening the question bank and my accuracy from question one was noticeably higher. The scenarios teach the reasoning pattern the exam rewards, not just what the right answer is.
I came to the CIPP/E from engineering with almost no legal background. The cram guide builds the GDPR structure from first principles — it does not assume you know what a recital is or how the supervisory authority structure works. By the end of week one I understood the framework well enough to reason through novel applications of it. Passed. The guide is accessible without being condescending.
I took the CIPP/E specifically to support a DPO appointment conversation with a client in Europe. The After You Pass guide has the exact Article 37(5) language — expert knowledge of data protection law and practices — and explains how to present the certificate as documentary evidence of that expertise. I used that framing with the client and they proceeded with the appointment. The guide is directly useful, not just motivational.
The deadlines quick-reference table — rights requests, 72-hour breach notification, Records of Processing threshold — every number the exam tests in one place with the article beside it. Printed it and kept it on my desk for the final week. Did not need to look at it in the exam. Four stars because the PDF typesetting could be cleaner.
First IAPP exam, no legal background. Was intimidated. The opening section on how the exam actually works — six formats, domain allocations, how Domain II carries the most questions, what command words signal — made the whole thing feel less unknown before I started studying content. Passed. The structural knowledge gave me confidence the content knowledge built on.
The toolkit section has a three-part LIA form — purpose test, necessity test, balancing test — based on the EDPB guidelines and structured around what regulators actually ask for. I adapted it for my organisation before I sat the exam. It is a better working template than anything I had found separately. The guide turns exam content into working documents.
Most question banks tell you the right answer. This one tells you what the question was testing, which distractor type each wrong option is, and why the right answer is right in that specific context. That is the information you need to learn from a wrong answer, not just know you got it wrong. I would have appreciated more questions specifically on the ePrivacy Directive.