
Under CIPP/E BoK v1.3.3, the 75 scored questions are spread across five domains, roughly: I. Introduction 7–13, II. Law and Regulation 18–28, III. Data Processing 13–21, IV. Scope and Accountability 8–18 and V. Compliance 8–16. Domains II and III together are more than half the exam, so they deserve about half your study time.
IAPP publishes question ranges for each domain in the CIPP/E Exam Blueprint. Using them to plan your hours, rather than studying topics in the order a textbook presents them, is one of the easiest ways to improve your result.
CIPP/E domain weights
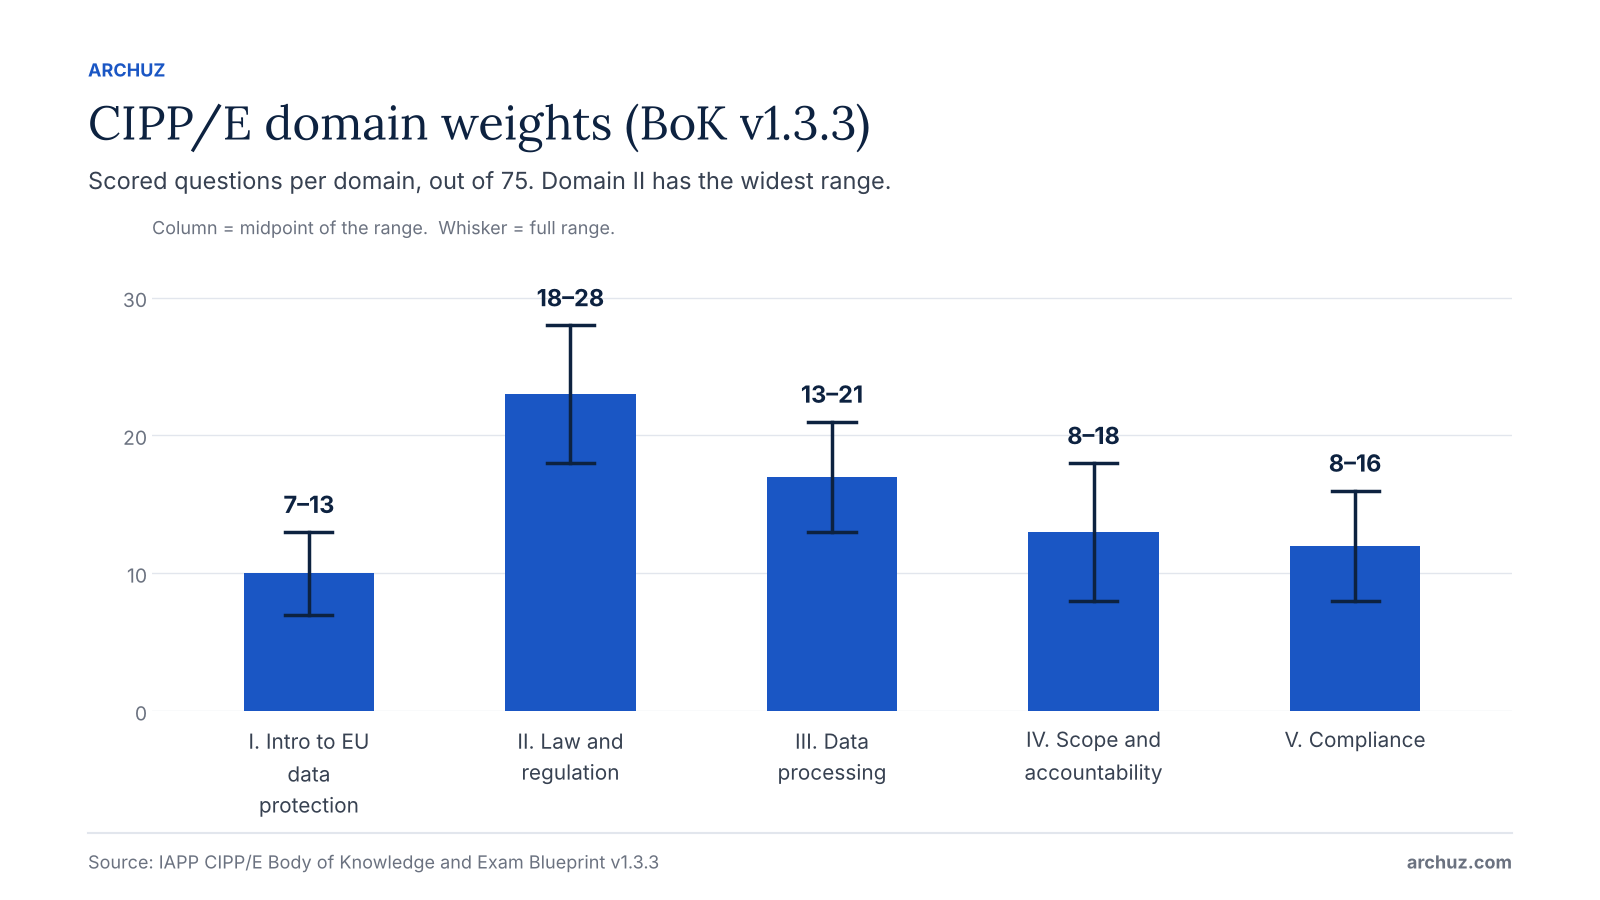
| Domain | Scored questions (approx.) | Approx. share |
|---|---|---|
| I. Introduction to European Data Protection | 7–13 | ~10–17% |
| II. European Data Protection Law and Regulation | 18–28 | ~24–37% |
| III. European Data Processing | 13–21 | ~17–28% |
| IV. European Data Protection: Scope and Accountability | 8–18 | ~11–24% |
| V. Compliance with European Data Protection Law and Regulation | 8–16 | ~11–21% |
Ranges are as reported from the v1.3.3 Exam Blueprint by study providers. IAPP's official blueprint PDF is the authority. Because the ranges overlap, your exact mix will vary by form.
Why the ranges look different from before
Before September 2025, the CIPP/E had three domains, and one huge Domain II covered most of the GDPR. In v1.3.3, IAPP split that domain into three (II, III and IV). IAPP says the change is organisational only: the number of questions per topic didn't change. If your old materials say "Domain II is 60% of the exam", that's the same content now spread across Domains II–IV. See BoK v1.3.3 changes.
Suggested study-hour split
| Background | I | II | III | IV | V |
|---|---|---|---|---|---|
| Baseline (by weight) | 12% | 30% | 24% | 18% | 16% |
| GDPR practitioner | 20% | 20% | 20% | 20% | 20% |
| Lawyer new to the GDPR | 10% | 30% | 25% | 20% | 15% |
| Non-lawyer (IT, security, ops) | 12% | 32% | 26% | 16% | 14% |
These are Archuz recommendations. GDPR practitioners often under-prepare Domain I (institutions and history), so a flatter split can help them.
What each domain rewards
- Domain I: memorisation of institutions, instruments and dates. These are quick points if you've reviewed them.
- Domain II: precise definitions, scope (Article 3), principles, and controller and processor roles.
- Domain III: applying lawful bases, special categories, transparency and rights to scenarios.
- Domain IV: accountability, security, breaches, DPIAs, DPOs, transfers and enforcement. This is the most table-friendly domain.
- Domain V: applied contexts such as employment, monitoring, marketing, cookies and AI.
High-yield topics within each domain
| Domain | High-yield topics |
|---|---|
| I. Introduction | ECHR Art. 8; Charter Arts 7–8; Convention 108/108+; EU institutions and their roles; ePrivacy Directive and Law Enforcement Directive basics |
| II. Law and Regulation | Art. 4 definitions; Art. 3 territorial scope; Art. 5 principles; controllers, joint controllers and processors (Arts 24–28); EDPB Opinion 22/2024 |
| III. Data Processing | Six lawful bases; legitimate-interest test (EDPB Guidelines 1/2024); consent conditions; Art. 9 special categories; Arts 12–22 transparency and rights |
| IV. Scope and Accountability | Security and breach notification (Arts 32–34); DPIAs (Art. 35); DPOs (Arts 37–39); Chapter V transfers; one-stop-shop and EDPB Opinion 04/2024; fines (Art. 83) |
| V. Compliance | Employment data; CCTV and monitoring; direct marketing; cookies (ePrivacy Art. 5(3)); AI and the GDPR |
Weights by background: adjusting the split
| Background | Spend more time on | Spend less time on |
|---|---|---|
| GDPR practitioner | Domain I (history, institutions); precise conditions in III and IV | Domain V contexts you handle daily |
| Lawyer new to privacy | Domains III and IV (lawful bases, rights, accountability, transfers) | Domain I, if you know EU law already |
| Technical or security professional | Domains I, II and III (legal concepts and language) | Security parts of Domain IV |
| Non-European candidate | Domain I and EU institutions; Article 3 scope | None. Follow the standard split |
A worked hour plan for 50 hours
| Domain | Hours |
|---|---|
| I. Introduction | 6 |
| II. Law and regulation | 12 |
| III. Data processing | 10 |
| IV. Scope and accountability | 8 |
| V. Compliance | 6 |
| Mocks and review | 8 |
Tracking your progress by domain
After each practice set, record your score by domain in a simple table. Re-plan weekly using the weighted-gap rule: put your next week's hours where the shortfall, multiplied by the domain's weight, is largest. Because your score report also breaks results down by domain, tracking this way means you'll be able to read it immediately after the exam.
See your score by domain
The CIPP/E Complete Pack's 300 questions are tagged to the five v1.3.3 domains, so you can track exactly where to spend your time.
Get the Complete PackDomain-by-domain warning signs
| Domain | You need more work if you... |
|---|---|
| I | Can't explain the difference between the ECHR and the EU Charter, or the roles of the Commission, Parliament and Council |
| II | Hesitate on whether something is personal data, or on Article 3 scope scenarios |
| III | Mix up Article 6 and Article 9 conditions, or rights' deadlines and exemptions |
| IV | Aren't sure when a DPIA or DPO is required, or which transfer tool applies |
| V | Can't apply cookie, marketing or employee monitoring rules to a scenario |
Frequently asked questions
Which CIPP/E domain has the most questions?
Domain II (European Data Protection Law and Regulation), with about 18–28 of the 75 scored questions.
How many domains does the CIPP/E have?
Five, under BoK v1.3.3, effective 1 September 2025.
Did the CIPP/E domain weights change in 2025?
The domains were reorganised from three to five, but IAPP says the number of questions per topic stayed the same.
Do I need to pass each domain?
No. You need an overall scaled score of 300, but weak high-weight domains make that much harder.
Should GDPR practitioners study Domain I?
Yes. Practitioners often under-prepare Domain I, which covers history, sources and EU institutions. It's usually easy points if you study it.
How do I know which CIPP/E domain to study more?
Use your practice scores by domain and simple self-checks: if you hesitate on scope, lawful bases, DPIA triggers or transfers, those domains need more time.
Sources
- OpenExamPrep: CIPP/E BoK blueprint (question ranges)
- IAPP: Q3 2025 annual updates
- Privacy Bootcamp: CIPP/E BoK 2025–2026
Last reviewed: October 2026.